
The Most Dangerous Risks to Your Business Don’t Swim on the Surface
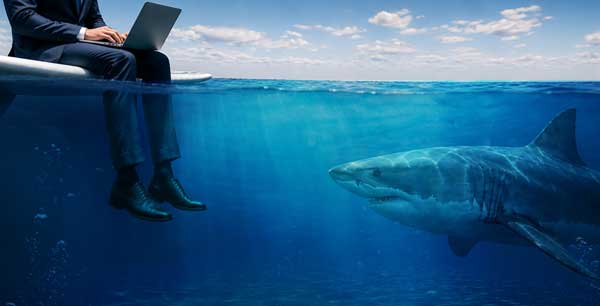
On the surface, the water looks calm. It’s what’s already moving underneath. Cybercriminals operate the same way. The threats businesses face right now are designed to blend in with normal operations until the moment something breaks, money moves, or systems go down.
During the summer, when schedules shift, employees travel, and oversight gets thinner, attackers know businesses are paying less attention. After 25 years protecting companies across the Triad, we see the same three things circling every July.
- Fake invoices and vendor impersonation
Attackers don’t need to hack anything. In many cases they just need to send one believable email. This is business email compromise (BEC), and it works by impersonating a vendor, supplier, or executive your team already trusts. The email looks completely normal, someone pays the “vendor,” and by the time anyone realizes the request wasn’t legitimate, the money is gone. These attacks spike during vacation season for a simple reason: when the person who normally approves payments is out, requests get rerouted to stand-ins who don’t always know what normal looks like.
The fix is simple: build a verification step for any financial request that arrives by email. A quick confirmation call to a known number — not the number in the email — stops most of these cold.
- Phishing that targets distracted employees
Phishing works because it’s engineered around how people behave when they’re busy. A distracted employee sees a password-reset notice and clicks. Someone gets a text that looks like it came from IT. An email lands right before a meeting asking for urgent approval on a wire transfer. Nobody stops to verify, because stopping feels like losing time. The most effective protection here isn’t software — it’s a culture where people feel comfortable slowing down when something seems off. Speed is the weapon attackers use against you; slowing down takes it away from them.
- Third-party risks that travel fast
When a vendor with access to your systems is compromised, the threat doesn’t stay contained to them — it travels straight into your environment through whatever connection they have. This is supply-chain exposure, and most businesses have far more of it than they realize: connected software tools, providers holding credentials, contractors whose access was never removed. Outsourcing a service doesn’t outsource accountability. Knowing where you stand means being able to answer three questions:
- Which vendors can access your data or systems?
- What exactly are they connecting to?
- Who internally is responsible for managing those relationships?
By the time you see it, it’s already moving
Sharks don’t announce themselves, and neither do the cybercriminals targeting your business right now. The companies that get hit aren’t always the ones ignoring obvious warning signs — they’re the ones who assumed everything was fine because nothing looked wrong. Summer is when schedules get loose, attention drifts, and the water looks calmest. It’s also when attackers are most active.
Our team helps businesses get a clear picture of where they’re exposed — across vendors, employee activity, and daily operations — before something goes wrong. If you’re not sure where your business stands, schedule a free 15-minute IT Foundation Check. Call (336) 904-9101 or visit solaceits.com.